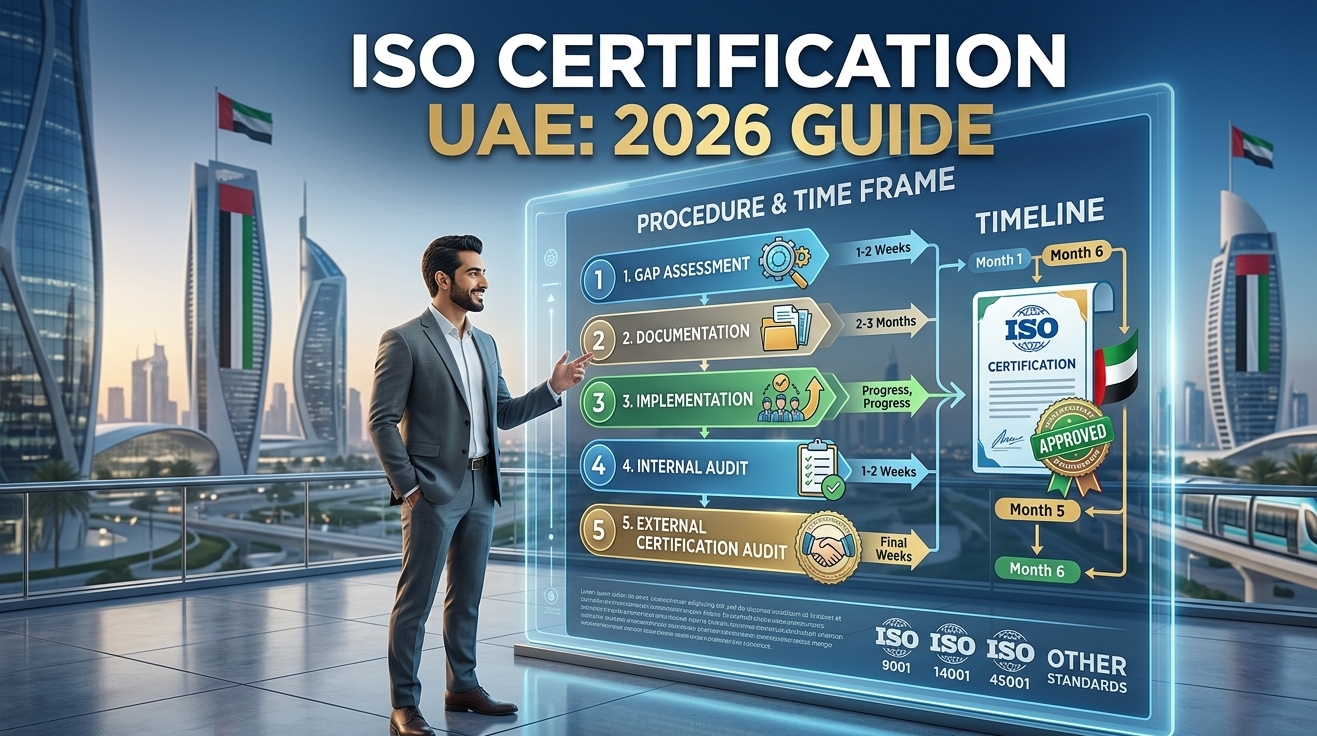
ISO Compliance in the UAE: The Complete Guide
Wiki Article
How Do You Choose The Most Suitable Iso Certification Business In Dubai
Dubai's market landscape is now no shortage of firms offering ISO certification services, which is very beneficial to clients, but it makes it more difficult to choose than it really needs to be. Understanding what actually separates a reputable certification company from one that's simply chasing volume makes a real difference to the value you get out of the process.Accreditation Is the First Thing to Check
An accreditation body's status is extremely important, as any certification issued by a company that's not accredited is of lesser value before auditors, customers, and tender assessors. It is vital to determine if a certification business is accredited by an established accreditation body, rather than just claiming that they issue internationally acknowledged' certificates, is the most significant early indicator.
Know the Difference Between Consultants and Certification Bodies
Many businesses misinterpret ISO consultants, who help in the implementation of a management plan, with certification bodies that independently review and issue a certificate for the certification. They are supposed to have distinct roles in order to protect that audit's impartiality in a firm that offers both of these services under one space for a client creates a legitimate conflict inter-dependence that merits being addressed directly.
It is the experience that counts.
A certified certification firm with genuine experience in your industry will ask sharper, more relevant questions throughout the audit process. Additionally, it will not apply checklist-like thinking for an enterprise with distinctive operational realities. Construction, healthcare and food production all present unique risks auditing an auditor who is not familiar with those particulars is likely to result in a less efficient certification experience overall.
Go Beyond the Headline Price
Certification pricing in Dubai Pricing for certification in Dubai is varied, and the least expensive option isn't always the best choice, however it's crucial to understand what's included before committing. Some quotes only cover the initial audit and exclude the required ongoing surveillance audits needed to maintain certification that can make a inexpensive price into a costly multi-year commitment than a competitive price which is more transparent.
You can ask questions about turnaround times in a realistic manner.
Businesses that are under time pressure, often because of the approaching deadline, often get lured in by the promise of quick approval. An audit that is properly executed takes at least a certain amount time, regardless of the degree of enthusiasm among all those involved and particularly fast timelines for turnaround are something to be considered skeptically rather than relief.
Review Reviews from businesses operating in Similar Industries
Feedback from other Dubai-based companies in a similar field can provide a more reliable information than generic reviews as it helps to understand how a company that certifies does its business in the less glamorous aspects of the process such as scheduling, document help, and handling irregularities discovered during an audit.
Inquire about Ongoing Support, Not Just the Initial Certificate
Certification isn't a single event It's a continuous process, requiring periodic surveillance audits and eventual renewal. A business that can provide unambiguous, systematic support throughout the year helps make the lengthy relationship much more smooth as opposed to one that focuses solely on winning the initial engagement.
Ask them about Multi-Site or Multi-Emirate Operations
Companies that operate across multiple locations within Dubai and across other Emirates, should inquire what kind of certification provider handles multi-site audits. Methodologies differ greatly among the providers. Some provide a truly integrated audit program covering all sites using a unified schedule while others consider each location as an individual engagement this can greatly impact both the cost and quality of the certification.
Understand the Difference Between UKAS, DAC, and other Accreditation Marks
Certification bodies that operate in Dubai may hold accreditation from a variety of national accreditation organizations, including UKAS which is located in the UK or the UAE's own Emirates International Accreditation Centre, and knowing which accreditation holds the most weight in relation to your specific clients and tender requirements is more important than assuming that every accreditation mark is acknowledged internationally.
Take everything in writing prior to when You Commit
Verbal assurances about scope, pricing, and timespan are not as valuable as an explicit written plan that outlines exactly what's included in the proposal, what happens when non-conformities get found, and what the costs will be over all three years of the certification cycle instead of the first audit. A reputable company will have no hesitation in supplying this level of detail prior asking for a pledge.
Be awestruck by the impressions you get from Initial conversations
Beyond checking credentials and pricing as well as pricing, the way a certified company handles initial inquiries frequently tells you a lot about how they'll be treated once you've signed a contract. An organization that responds to questions with clarity, doesn't press the customer into making a hurry decision, or appears concerned about your company rather than just selling a product is generally an excellent long-term companion than one focused purely on the speed of signing.
Paying Attention to High-Pressure Sales Tactics
Certain certification companies operating within Dubai's market compete with highly-pressured sales tactics, for example false urgency in relation to pricing with a limited time or claims they are in the process of negotiating with a competitor to secure a time slot. Certifying bodies that are legitimate do not have to be relying on this type of pressure because their value proposition relies on certification and track records rather than a blazing sales pitch, which makes pushy urgency itself a reasonable warning sign.
The best choice for a certification provider in Dubai comes down to verifying credentials in a proper manner, understanding the value you're paying for and prioritizing genuine experience over the lowest headline price for the certificate, as it is only as dependable as the method that made the certificate. The businesses that will get the greatest benefit from certification in Dubai aren't those who rely on the most affordable price, but those that decided to take the time evaluate accreditation, to understand the entirety of what they're buying, and pick a partner genuinely in tune with their market and size. Each of these tests takes long individually, but together they produce a thoroughly informed picture that helps protect against two most frequently occurring consequences of failing to choose the right partner: an not-usable certificate or an costly ongoing relationship. A little extra attention upfront is always worthwhile over the full multi-year certification relationship that follows. Have a look at the top rated ISO Certification Abu Dhabi for website advice.
ISO 27001 Certification: Protecting Data In A Digital-First Uae Economy
When the UAE economy continues to make the shift toward digital-first activities in government services, banking including healthcare, retail, and banking security has shifted beyond a pure technical IT issue to an actual executive-level concern. ISO 27001, the international standard for the management of information security systems, is now one of the most recognized methods for UAE enterprises to prove that they have taken their responsibilities seriously.What ISO 27001 Actually Covers
The standard offers a structured framework for identifying any information security risks, such as data breaches, cyberattacks physical security breaches, as well as internal process inefficiencies, and implementing appropriate controls to address them. Instead than imposing a tech solution, it calls for organizations to be aware of their own information assets and risks, then choose and implement measures in line with those risks.
The Reason UAE Businesses Are Putting It First
Beyond the increasing expectations of clients, UAE regulatory developments around the protection of personal data have led to a real institutional pressure to strengthen information security practices, particularly for businesses handling personal data related to financial records, healthcare records. ISO 27001 certification gives businesses a recognised, independently audited means to demonstrate their compliance instead of simply stating good security procedures internally.
Industries in which it carries a specific weight
Financial services, healthcare agencies, government-linked institutions, and companies involved in processing client data are all subject to a particular level of scrutiny over security of their information. the certification process has evolved to be close to a standard requirement in tender processes across these fields. Many businesses in adjacent industries that handle significant amounts of client information are striving for certification as well, acknowledging that the expectations of security for data are growing across the board rather than being limited to traditionally high-risk industries.
Its Risk Assessment Process Is Central
An honest, well-constructed risk assessment is at fundamentals of an effective ISO 27001 implementation, since all of the structure of the standard depends on the honest assessment of what their weaknesses are instead of using a generic security checklist. This usually involves categorizing the information assets of an organization, evaluating threats and vulnerabilities that affect each and prioritizing security measures based on the risk factor rather than ease of use.
Technical Controls Are Only Part of the Image
While firewalls, encryption and access control are important, ISO 27001 places equal importance to organisational security such as staff awareness education as well as clear emergency response procedures and the security requirements of suppliers. Most security issues stem from human errors or processes that are not working rather than being purely technical in nature this is the reason why the standards treat people and process controls with the same rigor as technology.
The Certification Process
Similar to other management-related standards, certification involves an initial gap assessment in the system, followed by the introduction of the necessary controls and documents as well as an internal audit and a 2-stage external audit from an accredited certification institution following by annual monitoring audits to verify that the system's integrity.
Ongoing Relevance in a Changing Threat Landscape
Security threats in the information industry are always evolving If a well-designed ISO 27001 management system is built around ongoing surveillance and development rather than a fixed set or controls created once and then discarded. Businesses that approach certification as a continuous process rather than a static achievement are more likely to have a stronger security posture over time.
Third-Party and Supplier Risks Attract serious attention
A large portion of information security incidents happen through third-party suppliers and partners, rather than a business's systems directly, for example, ISO 27001 requires businesses to genuinely assess and manage the security risk their supply chain introduces. This has led many certified UAE companies to stipulate security obligations in their supplier agreements, thus expanding their influence to the certification of the company.
The development of a true security culture That's Not Just Policies
The most effective ISO 27001 implementations go beyond creating policy documents. They actually incorporate security awareness into every day behaviors of staff, from how messages are handled to the way the physical accessibility to areas that are sensitive are secured. Auditors often probe understanding of staff by conducting audits in person, instead of solely relying on documentation review, making genuine commitment from staff a vital factor in successful certification.
Making preparations for Regulatory Alignment
A lot of UAE companies that have adopted ISO 27001 do so partly to prepare for alignment with a variety of local data privacy laws, as the standard's risk-based approach maps fairly well to the sort of accountability and control standards that are found in current data protection legislation. Certified companies are typically considerably better positioned to demonstrate compliance with the new regulations that come into force.
A Credential Signifying Genuine Professional
If partners and clients are looking to judge a UAE security level of a company's information, ISO 27001 certification signals something much more important than an internal statement that claims to take security seriously. It represents independent verification against a truly rigorous international standard. In a global economy that's increasingly built on digital trust, that certificate has real business value.
Handling Cloud Hosting and Third Party Hosting Concerns
Many UAE firms are now heavily reliant on cloud infrastructure and third-party hosting providers as well as ISO 27001 requires genuine assessment of the security risks that cloud infrastructure poses, rather than simply assuming the cloud provider you choose can cover all the essential security aspects. It is important to know exactly where the cloud provider's security liability ends and the certified business's responsibility begins is a detail that is a source of confusion for a huge number of new applicants.
For UAE companies operating in a growing digital-first marketplace, ISO 27001 certification offers an accreditation that can be competitive as well as more importantly, a legitimately structured system for managing the security risks for information that come with handling client and business information responsibly. With expectations for data protection continuing to rise throughout the UAE, businesses that make the investment in real security capabilities now are sure to be significantly better prepared for whatever regulations and clients' expectations are to come in the future. None of this needs to be done in a single day, as a phased approach to implementation, prioritising the highest-risk areas first, tends to produce an even more solid, firmly in-built security culture rather than attempting all things simultaneously under the pressure of time. Businesses that begin this process earlier rather than later usually have a better chance of being prepared for whatever comes next. Security, when approached this way can become a significant competitive advantage rather than being a defensive cost centre. The change in frame of reference changes how the entire project is allocated internally. The companies that realize this earlier are the ones that benefit the most. Follow the top rated ISO Consultants Dubai for website info.